1. Evidence intake with lineage
Your scanners, certificate tools, and external-risk feeds all produce signals. ThreatWarden connects them into one workflow — with ownership, triage, exceptions, and proof built in.
Turn security signals into accountable actions, track SLAs, and automatically generate the evidence required for NIS2, DORA, and SOC 2 compliance - without slowing down your IT team.
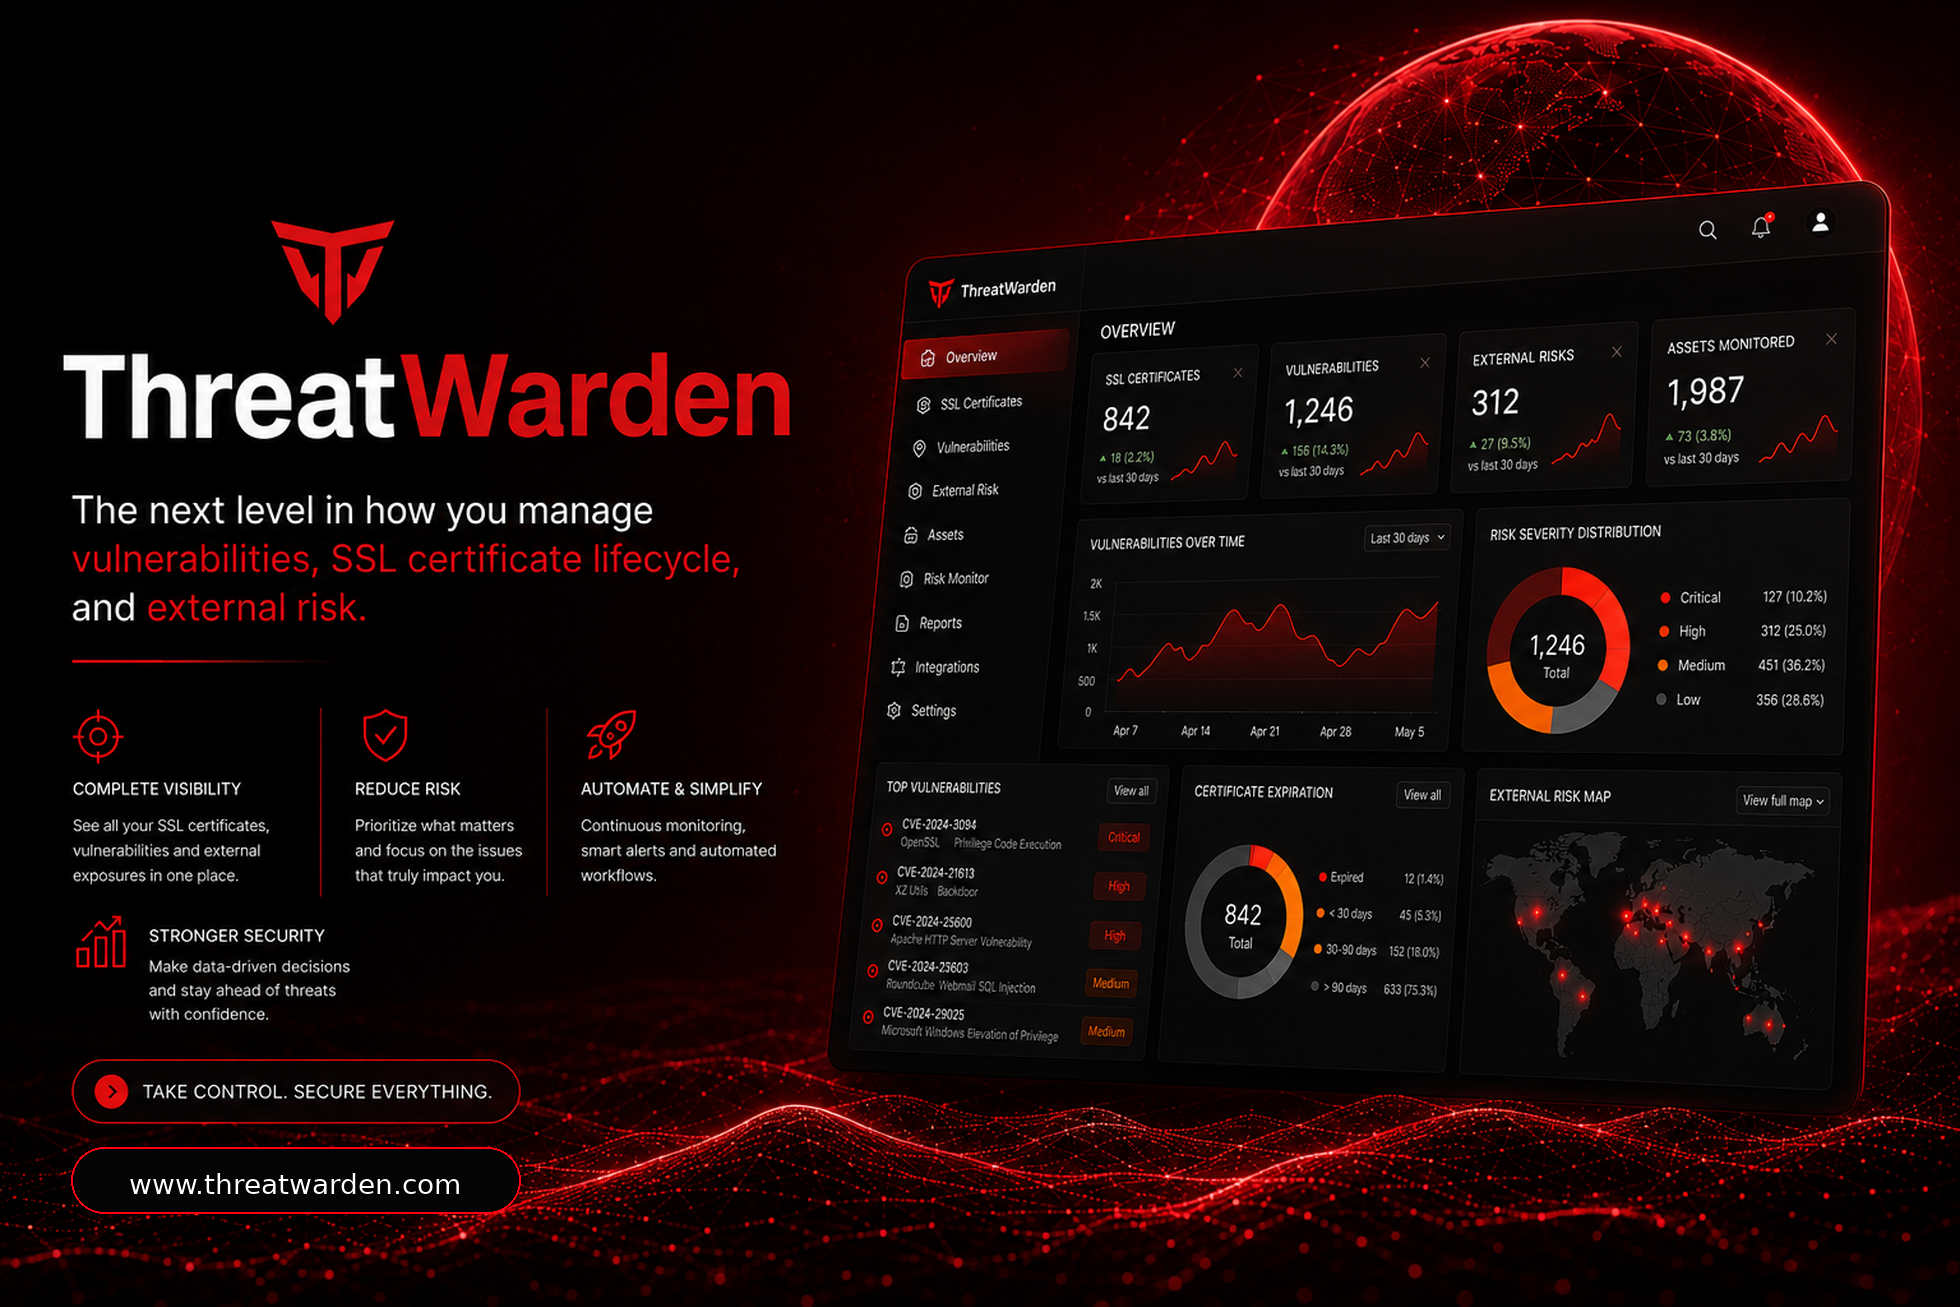
Product model: how ThreatWarden works
For teams that already receive security findings and risk signals, but cannot consistently prove ownership, remediation, exceptions, certificate hygiene, and executive readiness.
Your scanners, certificate tools, and external-risk feeds all produce signals. ThreatWarden connects them into one workflow — with ownership, triage, exceptions, and proof built in.
Raw signals are normalized into assets, findings, certificates, external signals, owners, queues, work items, exceptions, and verification records.
Instead of separate dashboards per tool, teams get one explainable workflow with severity, age, asset context, duplicate handling, blockers, due dates, and ownership.
AI can summarize context and suggest direction, but approvals, exceptions, accepted risk, and remediation accountability stay owned by the team.
ThreatWarden tracks open, blocked, accepted, assigned, fixed, verified, and improving work, so reports are based on operational proof instead of spreadsheets.